THM: Neighbour
Check out our new cloud service, Authentication Anywhere. Can you find other user’s secrets?
This room is all about insecure direct object references or (IDOR).
Running initial fast scan to identify open services:
1
sudo nmap -T4 -sS -p- --min-rate=10000 TARGET_IP
Results
1
2
3
PORT   STATE SERVICE
22/tcp open  ssh
80/tcp open  http
Heading to http://TARGET_IP we’re met with a login page 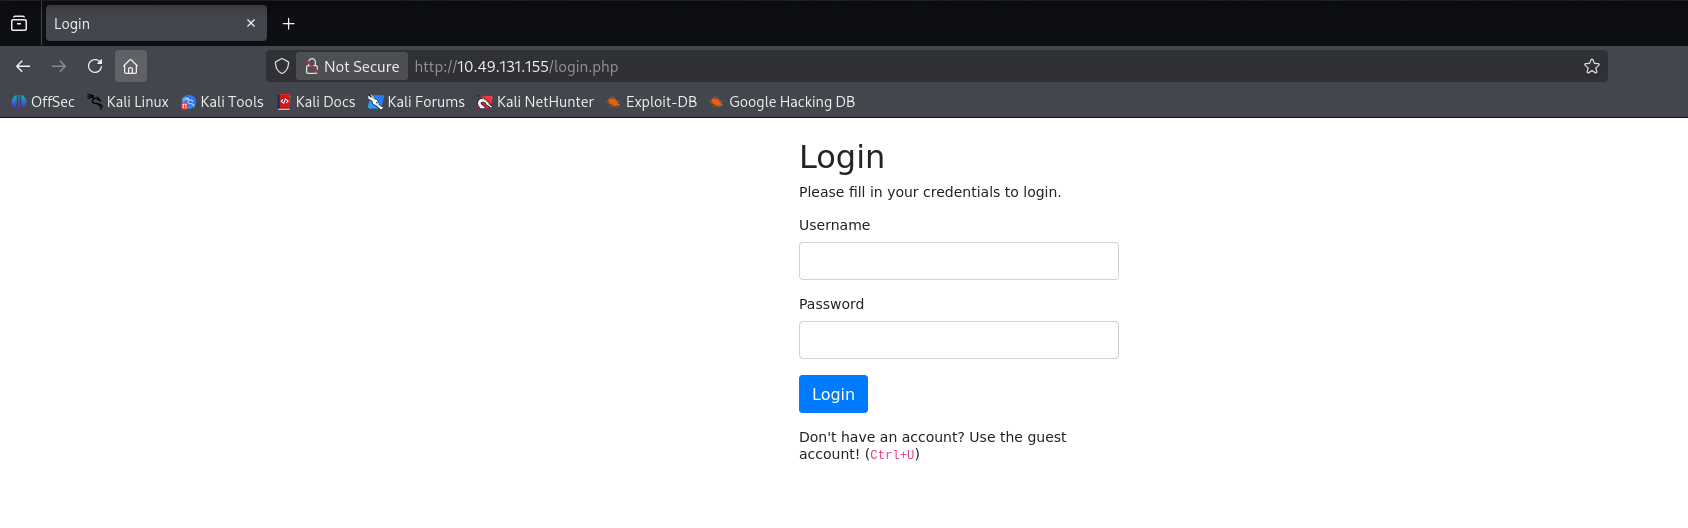
Viewing the page source shows how to login
1
2
<p>Don't have an account? Use the guest account! (<code>Ctrl+U</code>)</p>
<!-- use guest:guest credentials until registration is fixed. "admin" user account is off limits!!!!!
Loging in via guest:guest shows a vulnerable path
1
http://TARGET_IP/profile.php?user=guest
Lets see what happens when we change user=guest to user=admin 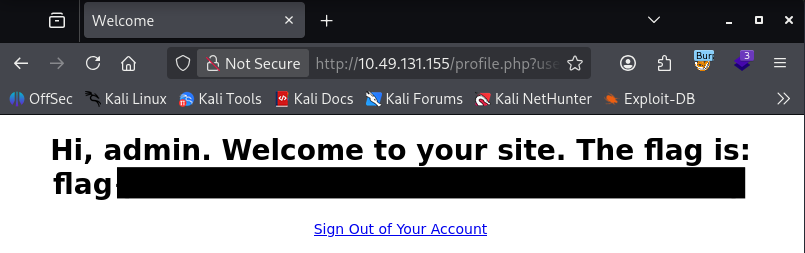
Thats all for this room folks.
| Room: Neighbour | Platform: TryHackMe | Difficulty: Easy | Access Method: IDOR |
This post is licensed under CC BY 4.0 by the author.